One graph. Every question you'd otherwise ask eight tools.
AuditGraph is not a collection of tools that happen to share a login. Every surface renders the same canonical facts, produced once, by one owner. If two screens disagree, that is a defect — not a perspective.
Early access · Read-only access · Plans from $9,000/year
Read-only consent to ranked decision in four steps.
Grant read-only access
Admin consent to read-only Microsoft Graph permissions and the Azure Reader role. No agent is installed. AuditGraph never changes your tenant on its own: the only change is the read-only Reader role your administrator grants at sign-up.
Discovery builds the graph
Every identity across every class — human, service principal, managed identity, workload, CI/CD, PAT, OAuth app, AI agent — with role assignments, scopes, federated credentials, and PIM state.
Engines compute consequence
Reachability, blast radius, attack paths, and data exposure — derived from configuration, not inferred from behavior. Each identity receives a lineage verdict.
One ranked decision
Ranked by business consequence — never by population or node count — with the evidence trail attached, ready to hand to an auditor.
Three ways into the same graph. Pick the question you have.
Identity Graph
If this identity were compromised, what could it trust, reach, influence or put at risk?
Ranked by the server: Tier-0 standing, privileged authority at the root, who can grant access and who can escalate, each with its candidate paths.
Access Graph
What can this identity do, and who else has the same access?
One identity through its groups and role assignments to every scope and resource it reaches — direct, group, inherited and PIM-eligible drawn apart — as a graph, by role, by resource, a path or a table.
AuditMap
Who can access this asset, and exactly how?
Pick a management group, subscription, resource group or resource: every identity with access there, inherited access included, and what was not collected. Its what-if simulator (Professional and Enterprise) models removing a grant before anyone changes it.
Seven screens. One decision.
The product itself, on a synthetic demo tenant. Step with the buttons, the numbered tabs or the arrow keys.
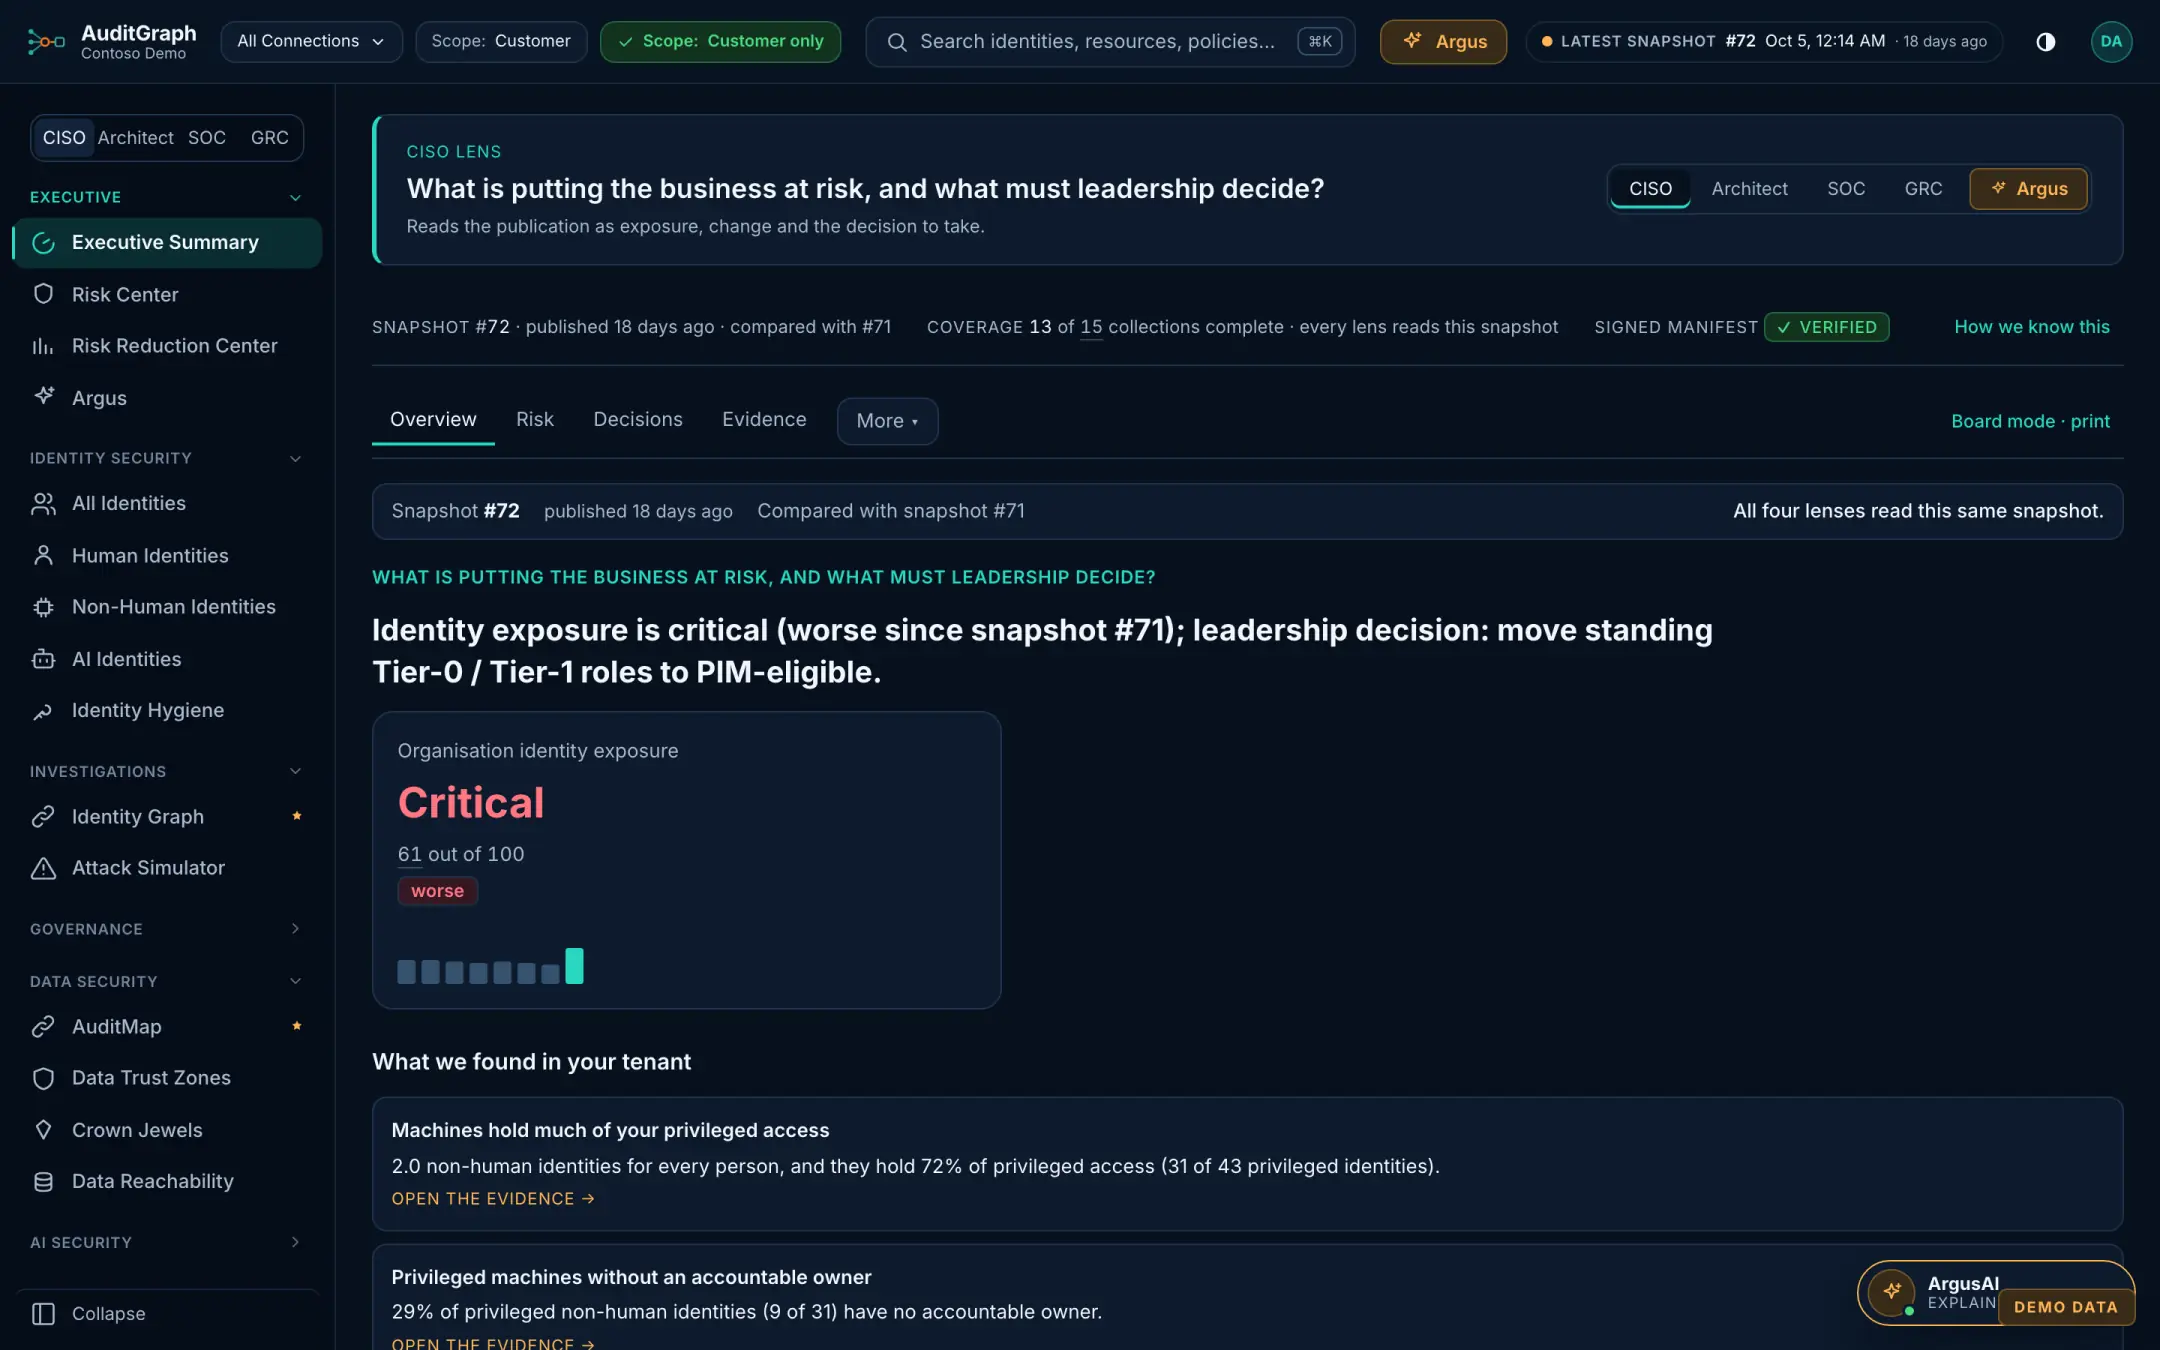
The briefing: one question, one answer
Each lens opens on its question, a one-sentence answer and the decision to take — read from one signed, published snapshot, with coverage stated.
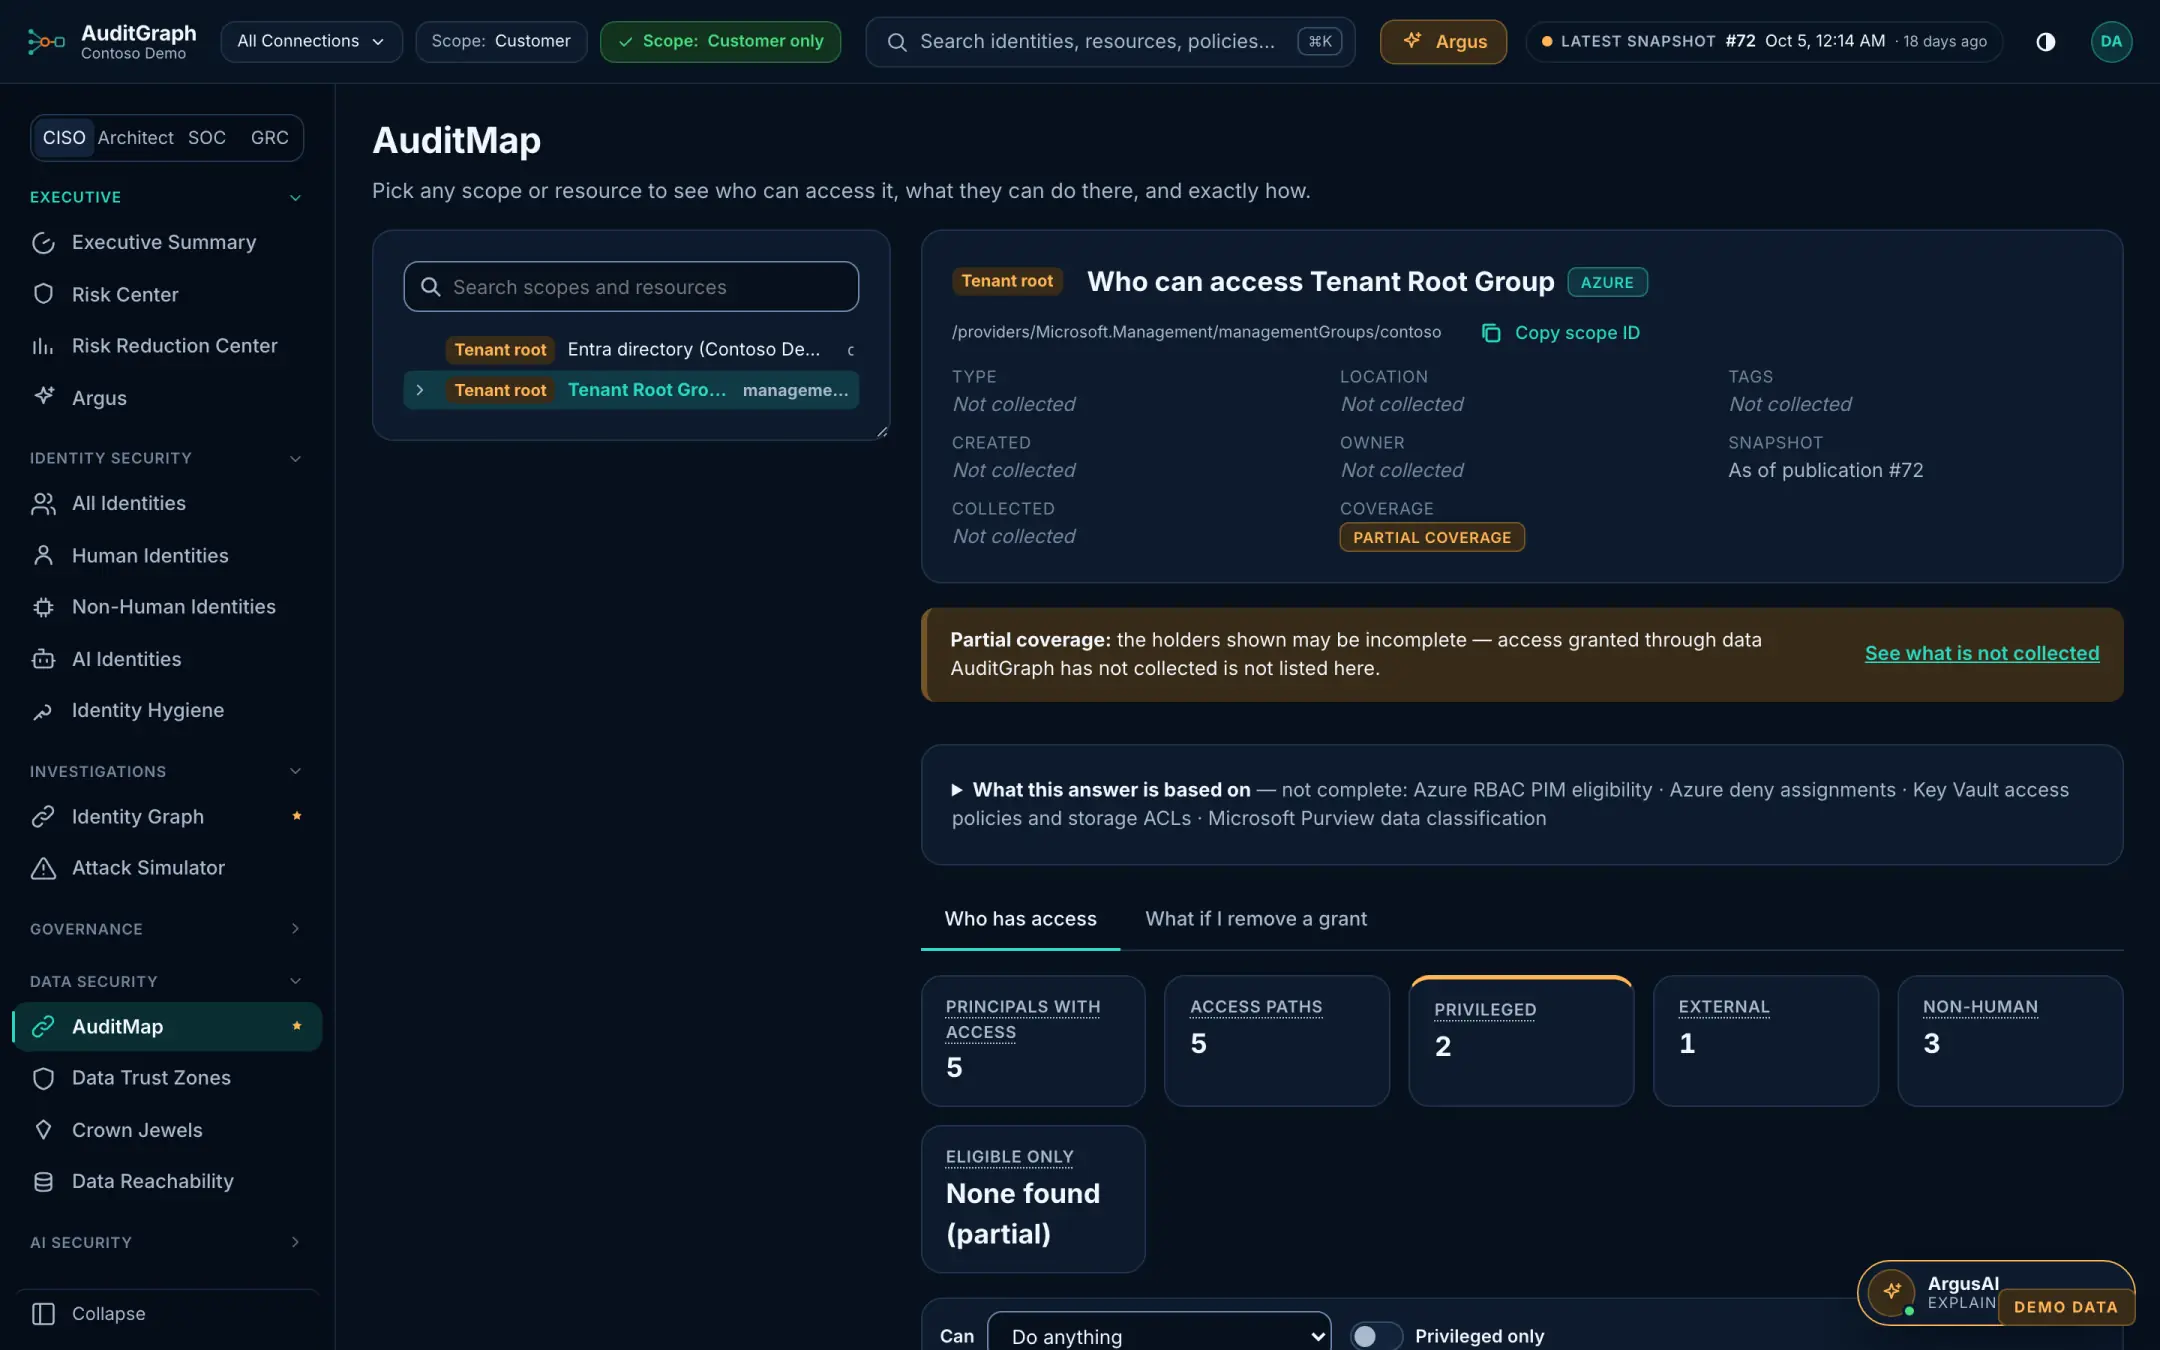
AuditMap: start from the resource
Pick a management group, subscription, resource group or resource and see every identity that can reach it, inherited access included — and what was not collected. Its what-if tab models removing a grant before anyone changes it.
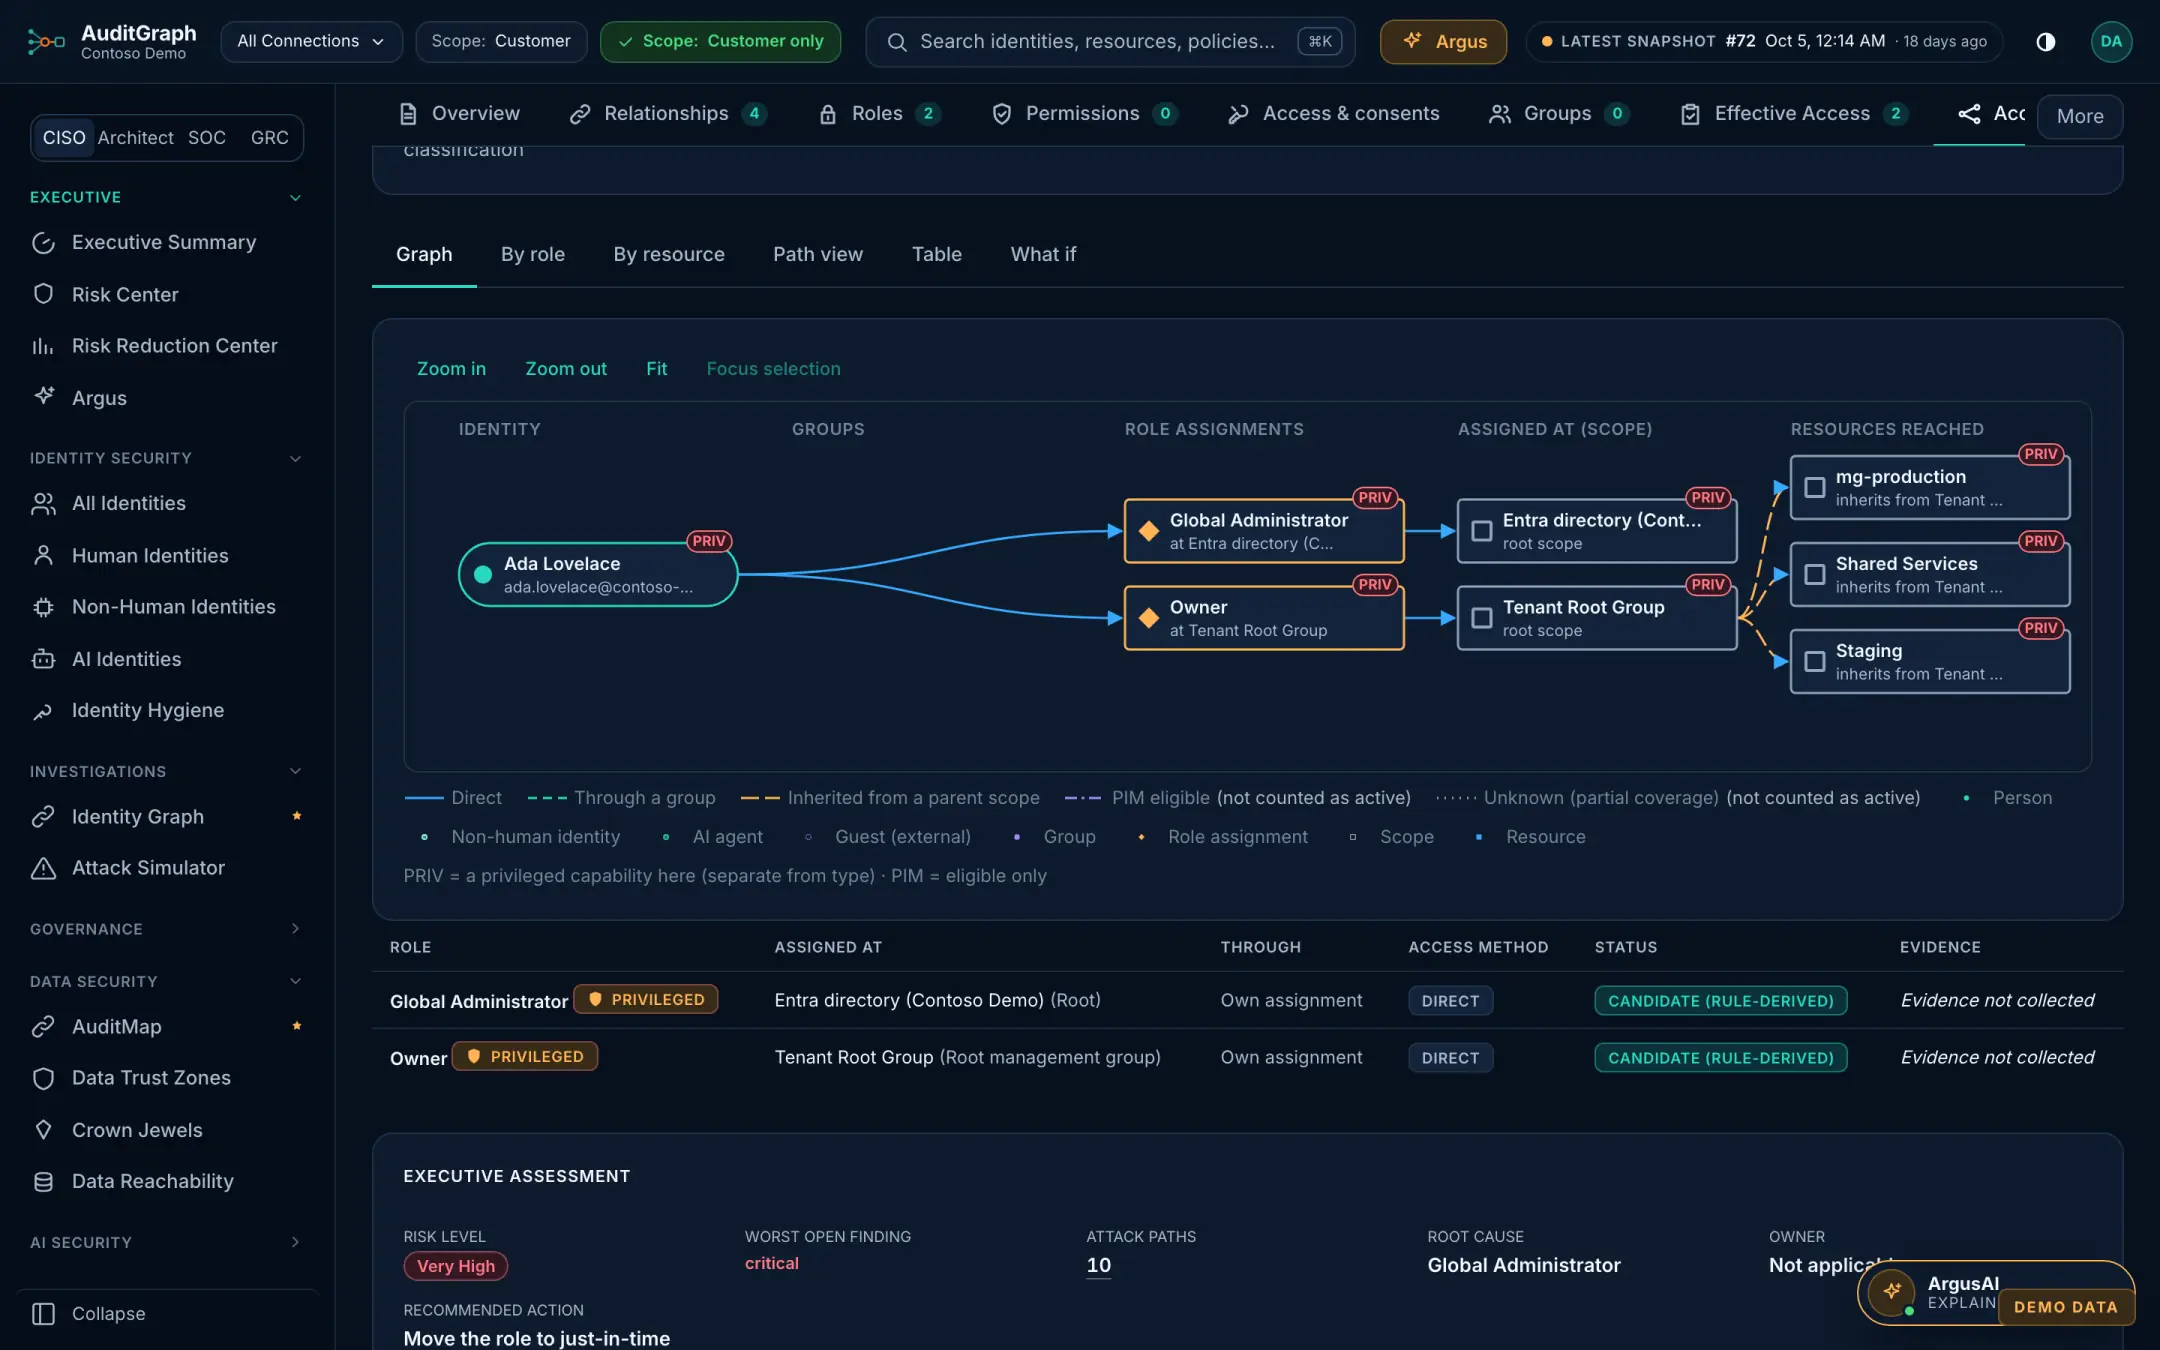
Follow one identity to everything it reaches
Identity → role assignment → scope → the resources it inherits, with direct, group, inherited and PIM-eligible edges drawn differently.
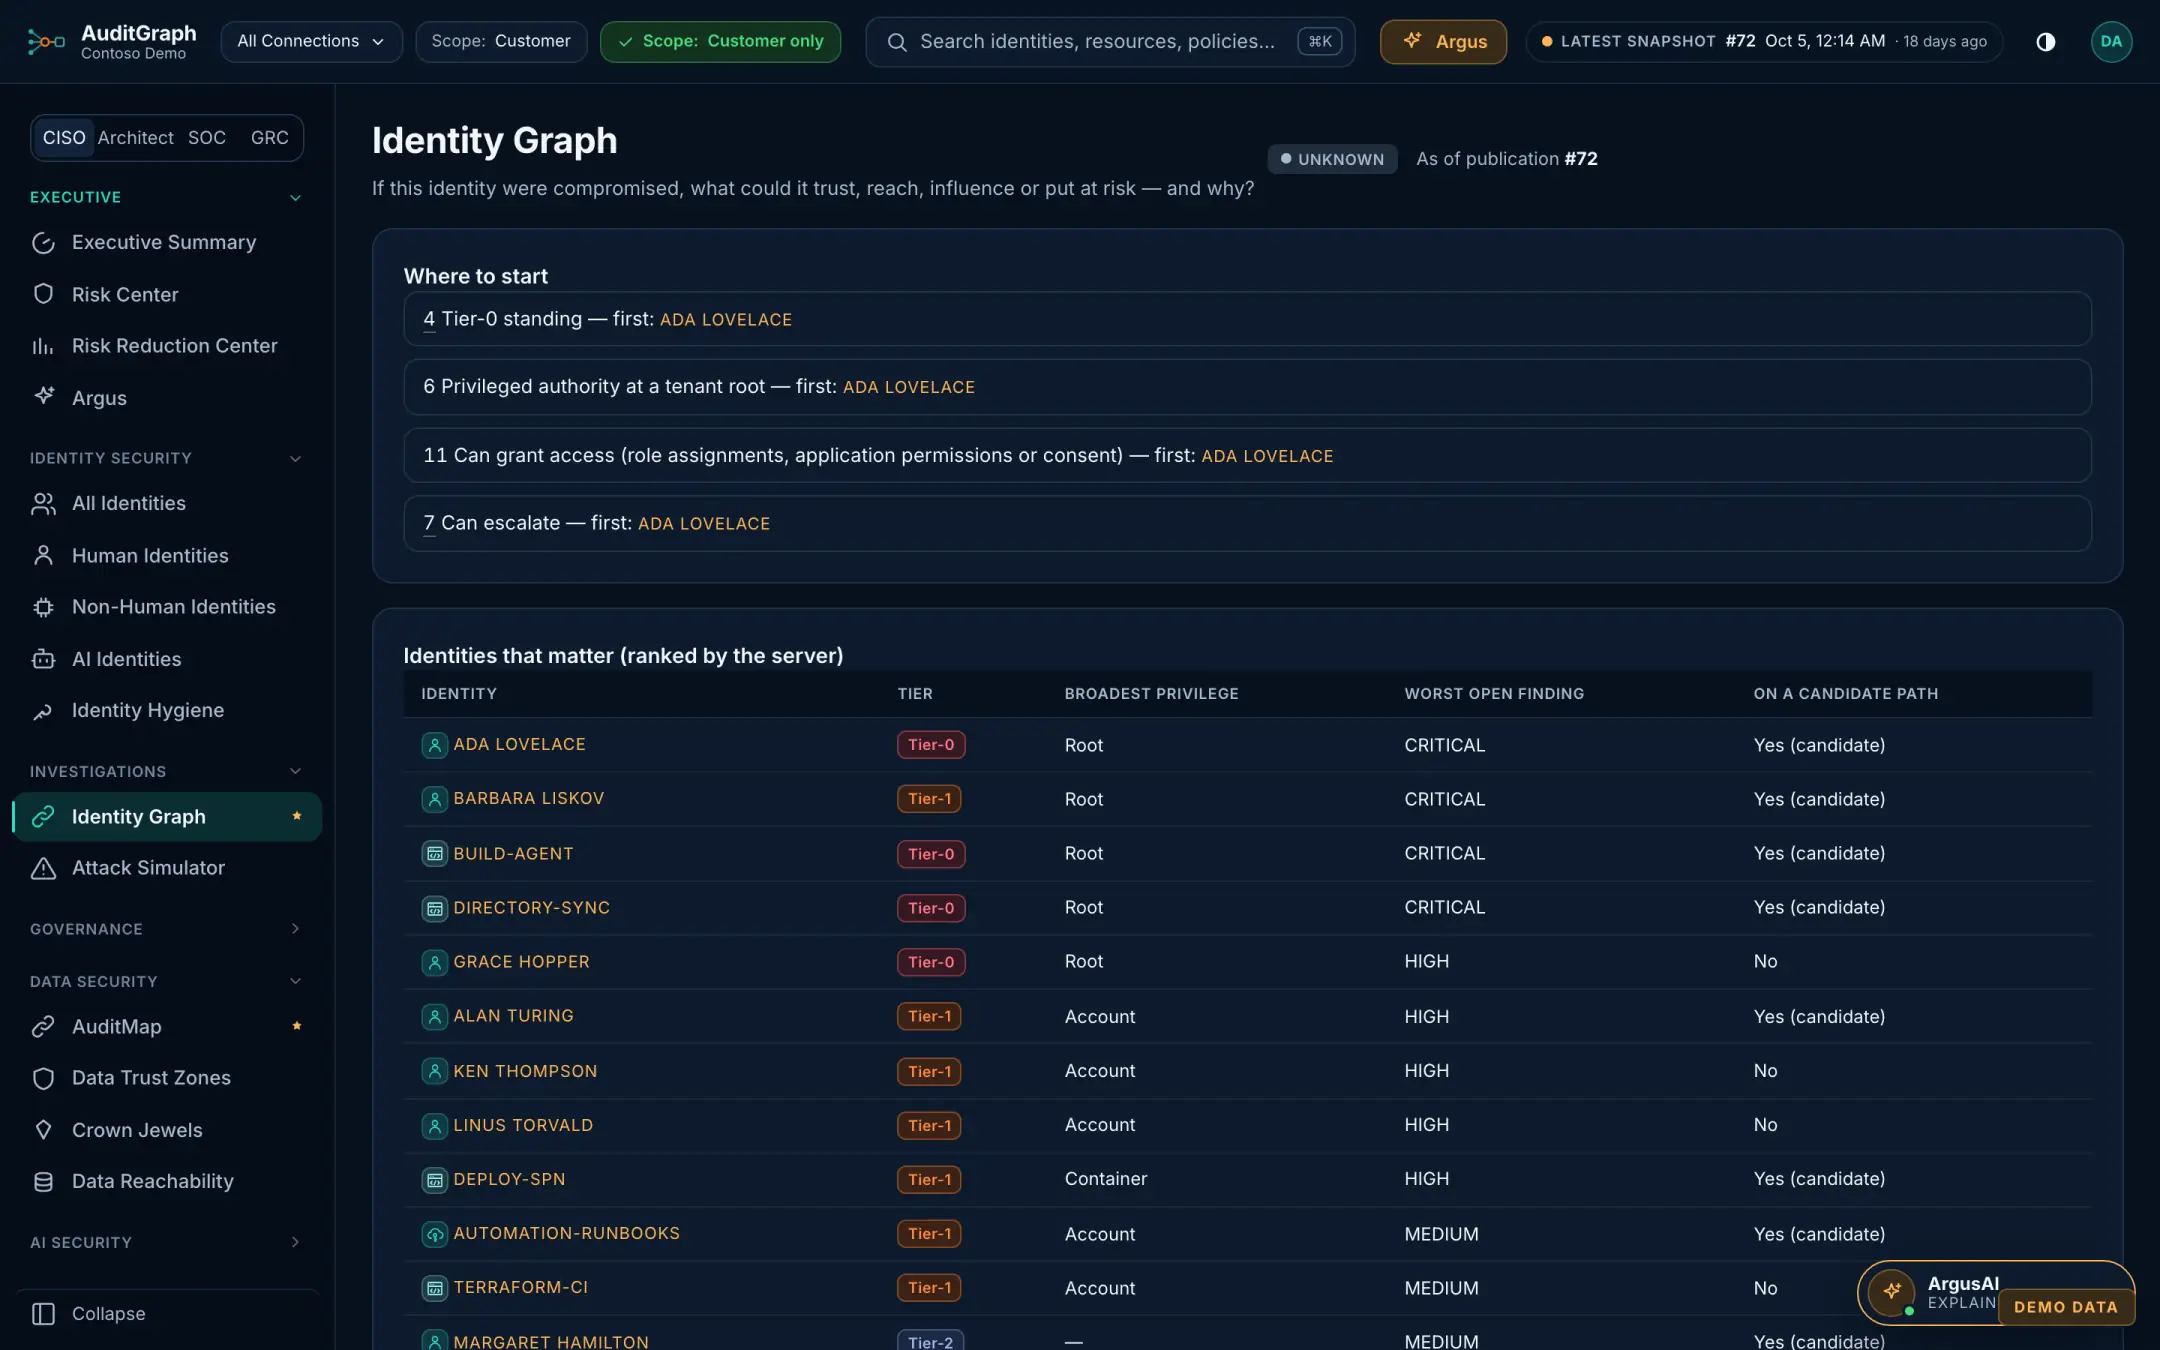
Where to start, ranked
Tier-0 standing, privileged authority at the root, who can grant access and who can escalate — ranked by the server, each on or off a candidate path.
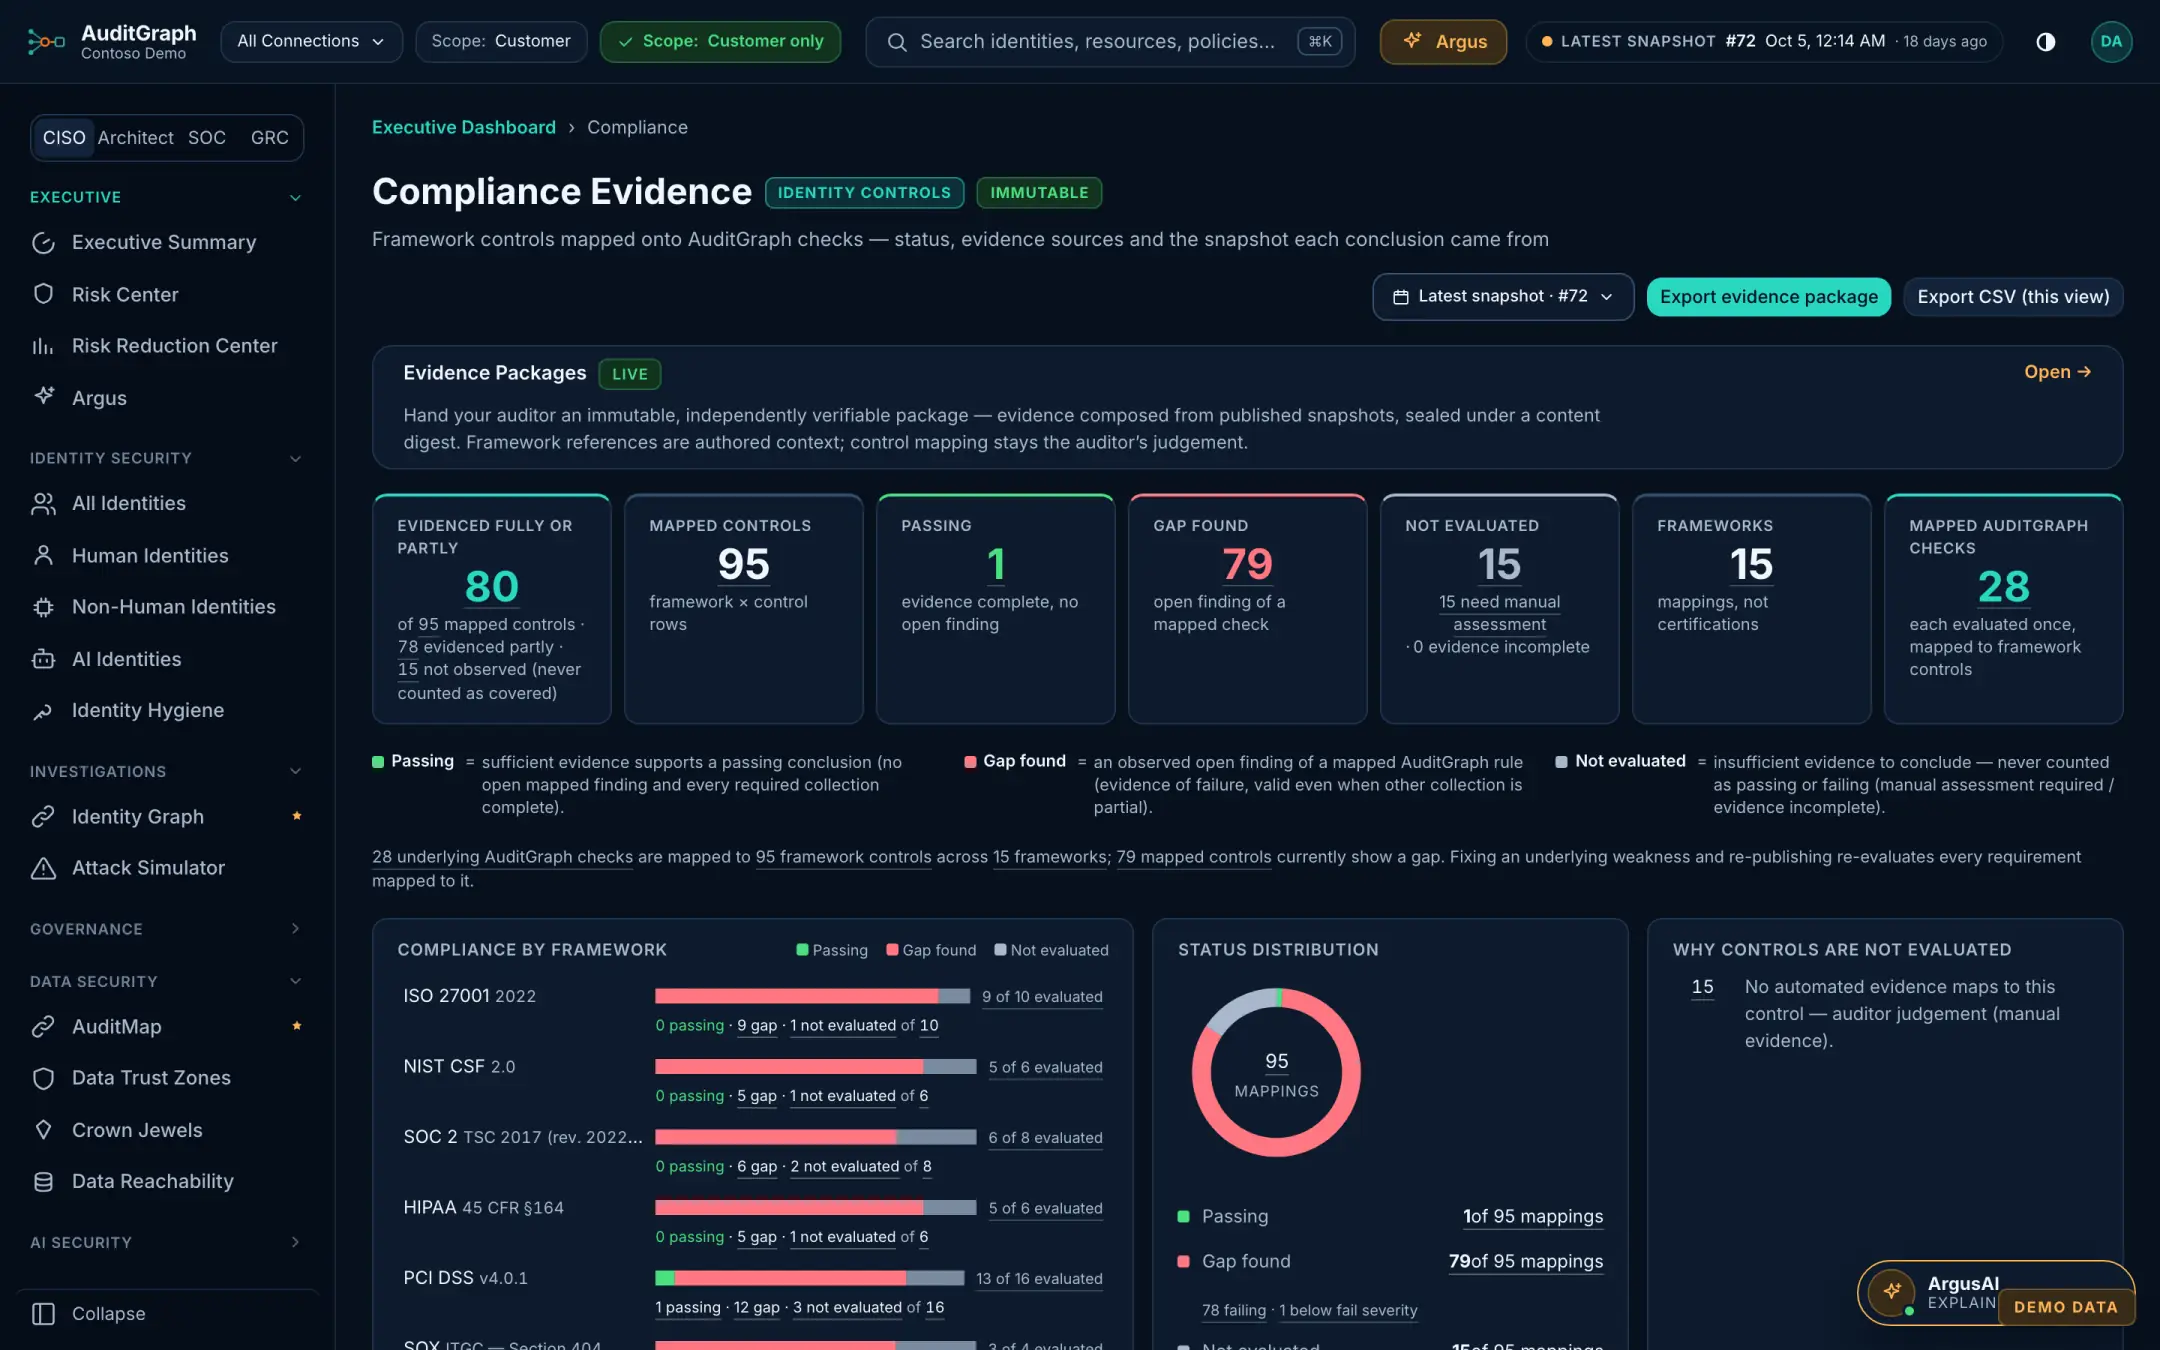
Controls mapped to evidence
Framework controls mapped onto checks: passing, gap found, or not evaluated — and not-evaluated is never counted as covered.
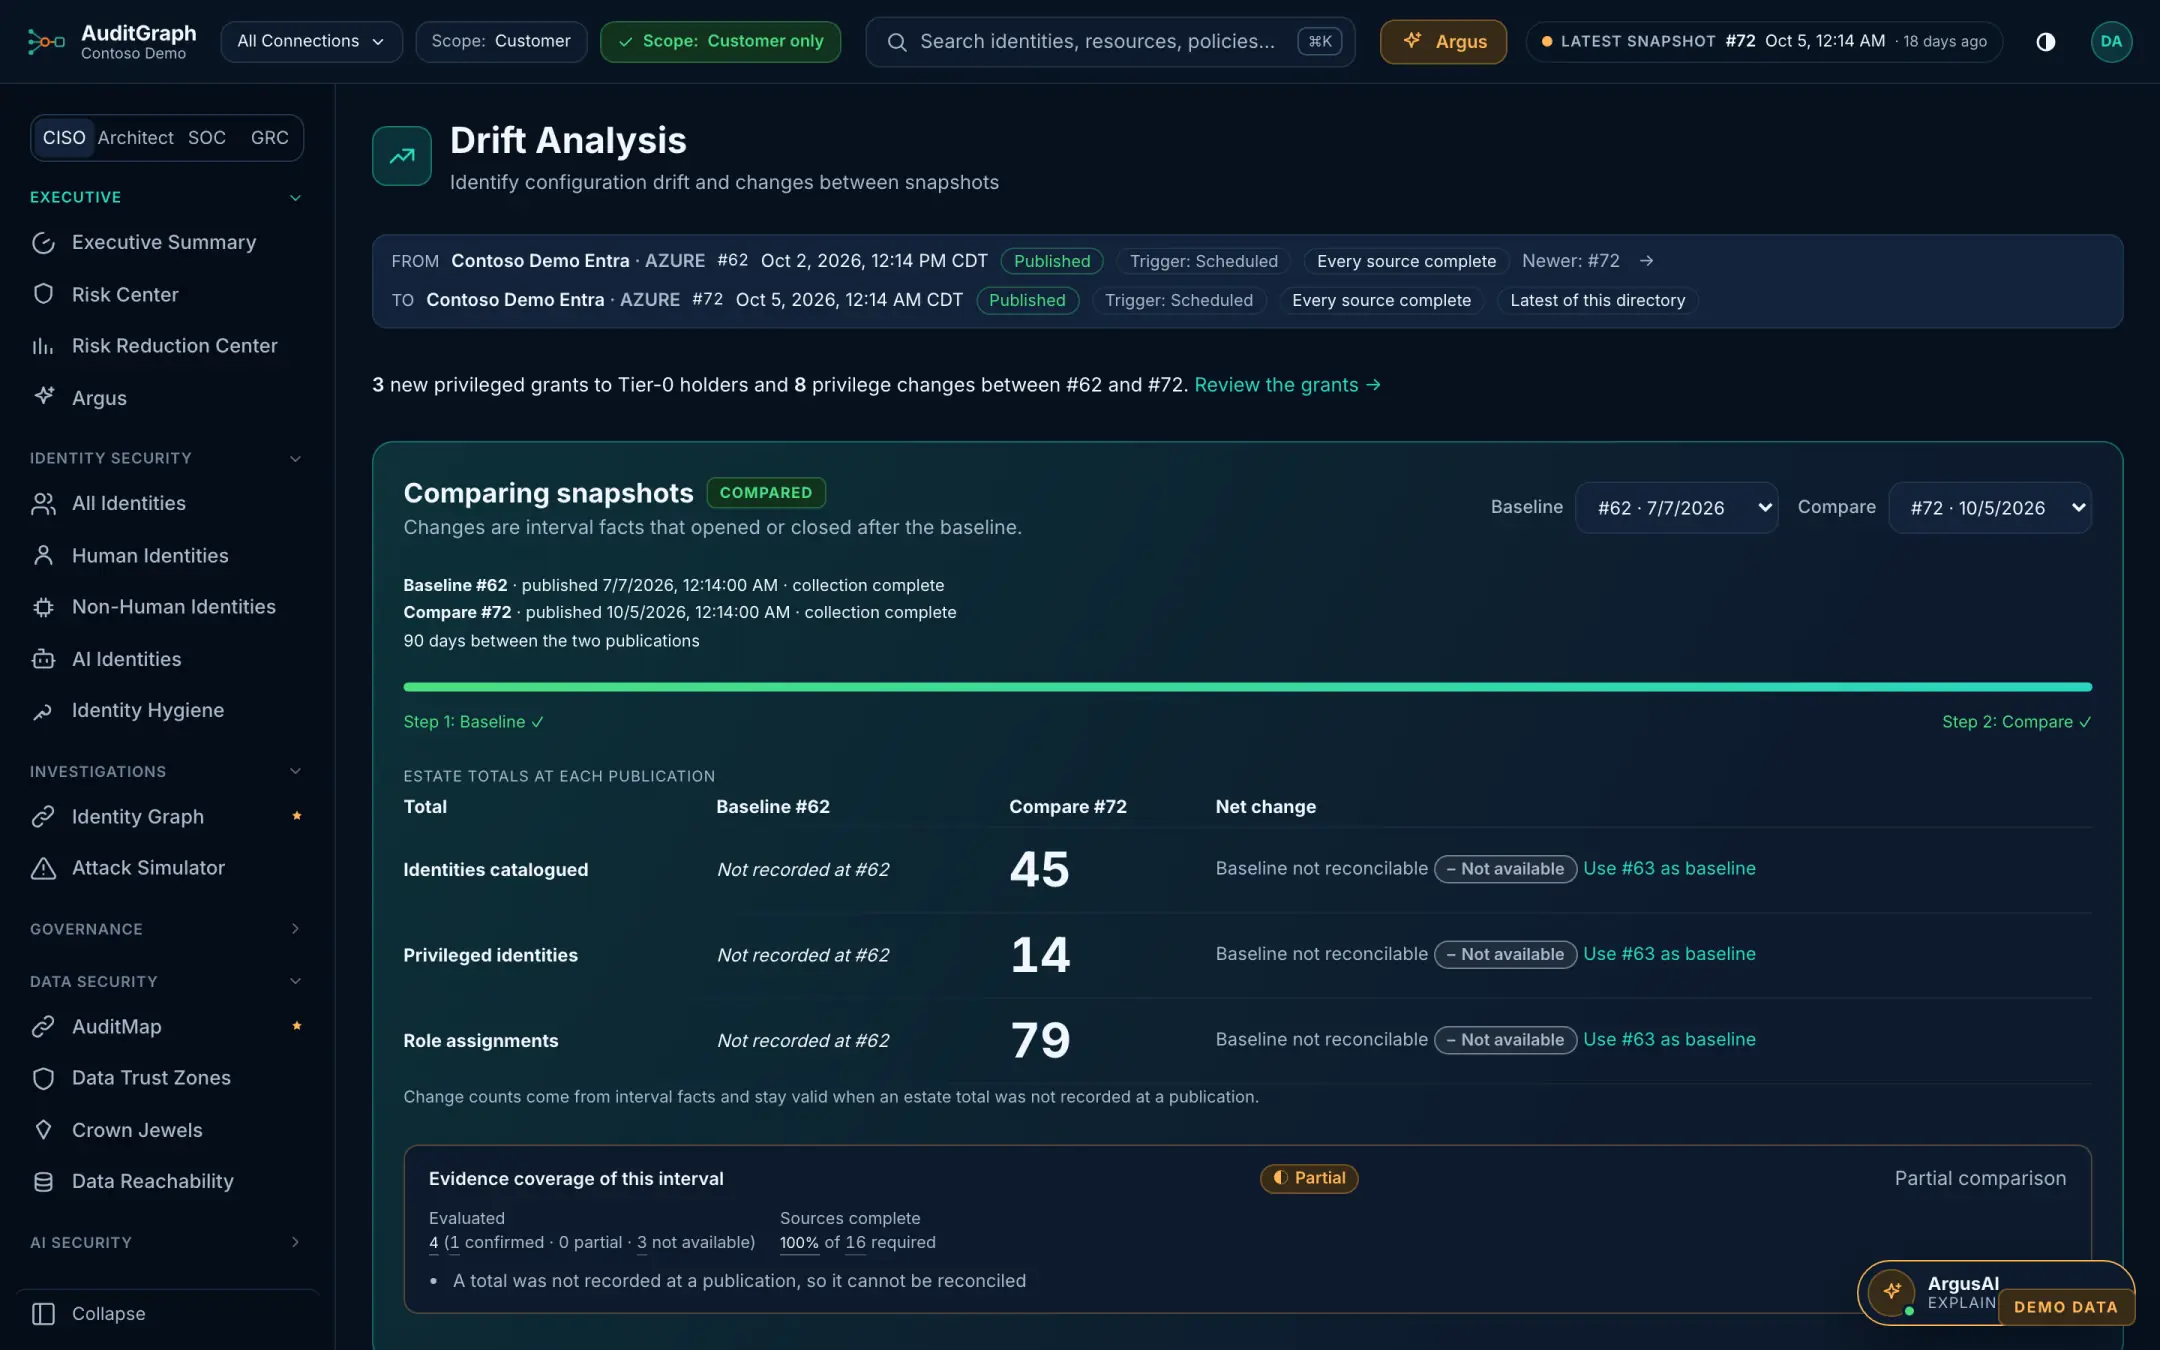
What changed between snapshots
Two published snapshots compared: new privileged grants, privilege changes, and where a baseline cannot be reconciled it says so.
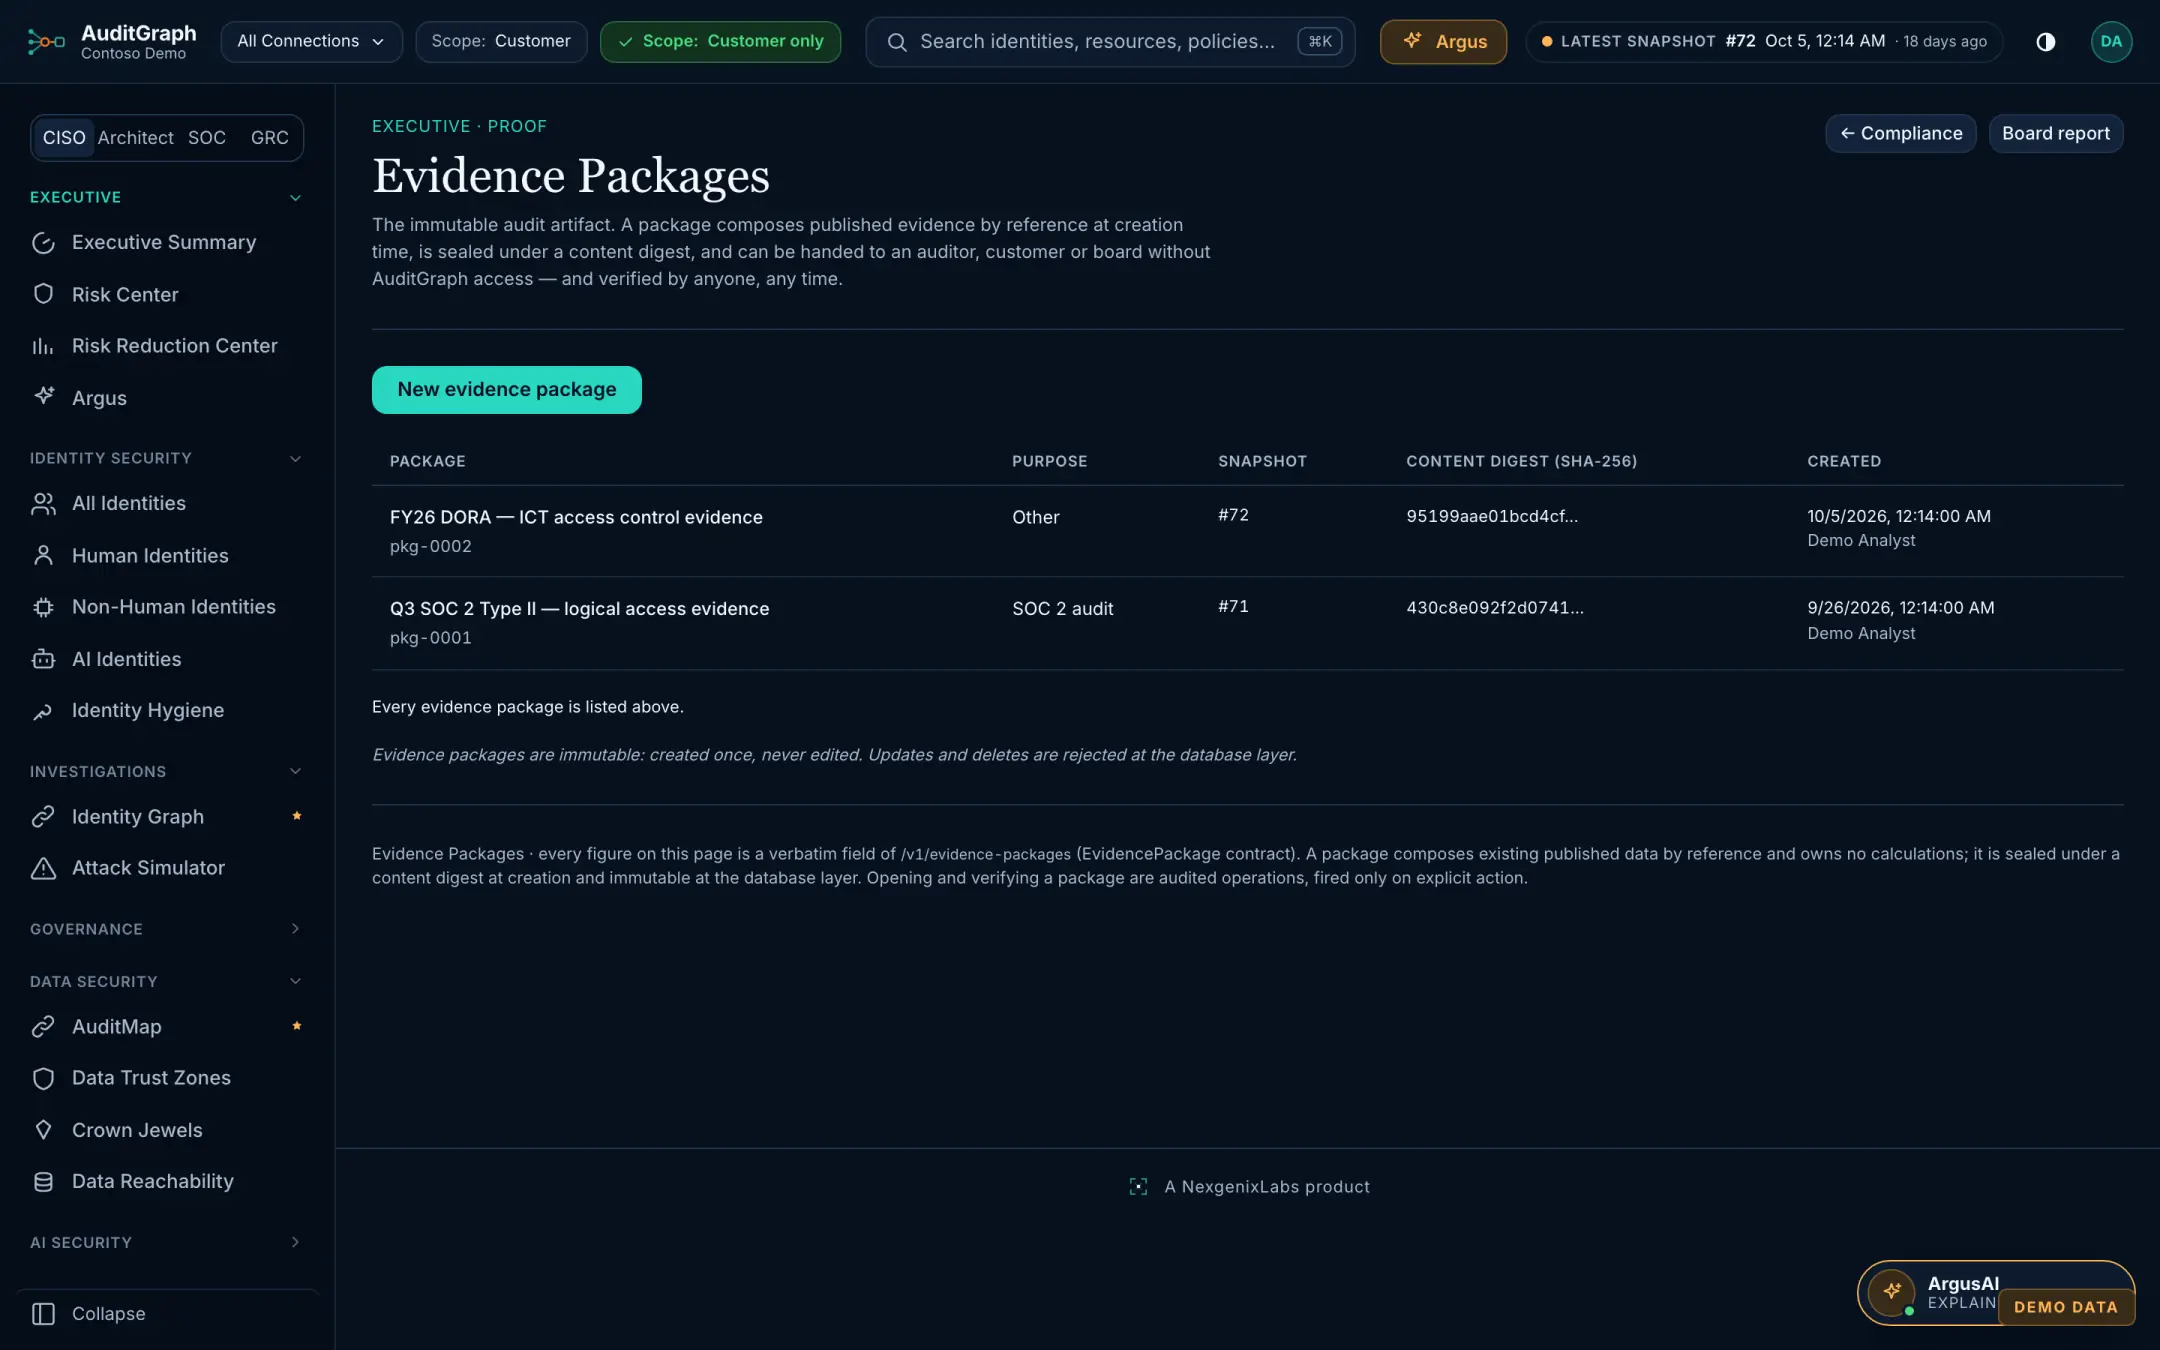
Evidence an auditor can verify
Immutable packages sealed under a SHA-256 content digest, handed to an auditor or board and verifiable without AuditGraph access.
Every capability — and exactly how mature it is.
Maturity below is copied from our internal feature catalog, not written for this page. GA ships and reconciles. Alpha is usable but not yet trustworthy for a buying decision. We would rather you know.
Decision Center
What is the biggest identity risk to the business today, and what is the one move?
Identity Security
Who and what exists, what do they hold, and when was it last used?
Investigations
How would an attacker get from here to something that matters?
Governance
Where is privilege excessive, and who signs off on reducing it?
Data Security
Who can reach our regulated data, and by what path?
AI Security
What AI is running in our tenant, and what can it reach?
Compliance
Can we prove this to an auditor?
Operations
Is what I am looking at fresh, and what changed?
Reads from Microsoft. Reports into the tools you already run.
- Microsoft Entra ID
- Microsoft Azure
Read-only. Azure is the generally available cloud; AWS and GCP are roadmap.
- Slack
- Microsoft Teams
- Signed webhooks
Change alerts on every plan, including the evaluation.
- Jira
- ServiceNow
- Azure DevOps
Ticket workflows on Professional and Enterprise.
- Azure Monitor
- Microsoft Sentinel
- Splunk
- Datadog
- Elastic
- Sumo Logic
Findings export on Professional and Enterprise.
Product names are trademarks of their owners and are used only to describe compatibility. No endorsement or partnership is implied.
What we don't do yet, in writing.
This list lives at Trust → Known limitations and is maintained alongside the product, not the marketing.
Find the reach you never granted.
A scoped assessment against your own Azure tenant. Read-only, always: AuditGraph never changes your tenant on its own.
Early access · Read-only access · Plans from $9,000/year
Read-only access · No agents · No log ingestion · Azure generally available